
Mastering Strong Password Security and Passphrase Strategy
When your passwords or passphrases are weak, you provide unauthorized actors with an open door into our internal network and client infrastructure.
Why this matters
When your passwords or passphrases are weak, you provide unauthorized actors with an open door into our internal network and client infrastructure. A single compromised account at a distributor like ours can lead to widespread data breaches, loss of confidential dealer pricing, and the degradation of our reputation with top-tier technology vendors.
The core idea
At the heart of cybersecurity is the concept of entropy, which refers to the level of unpredictability in your credentials. A password is a string of characters used to authenticate access to a system. A passphrase, by contrast, is a long sequence of words or phrases that acts as a significantly more secure alternative to traditional complex passwords. While traditional requirements often forced employees to use a mix of uppercase letters, lowercase letters, numbers, and symbols—often resulting in short, predictable strings—modern security standards emphasize length over complexity.
Brute-force attacks, which are automated processes where a computer program attempts to guess every possible combination of characters, are far less effective against long strings of random words because the mathematical number of possible combinations grows exponentially as characters are added. By choosing a series of unrelated words, you create a credential that is easy for a human to memorize but statistically impossible for current decryption software to crack within a reasonable timeframe.
How it works in practice
When you are securing administrative access to a telecom appliance, such as an IP-PBX system or a cloud management portal like Cisco Meraki or FortiCloud, you must prioritize length. For any business tool we use, aim for a minimum of 16 characters. Instead of thinking in terms of character sets, think in terms of distinct words. A reliable method is to pick four or five random words that have no logical connection, such as "Blue-Coffee-Truck-Keyboard." This provides the high entropy required to thwart credential harvesting.
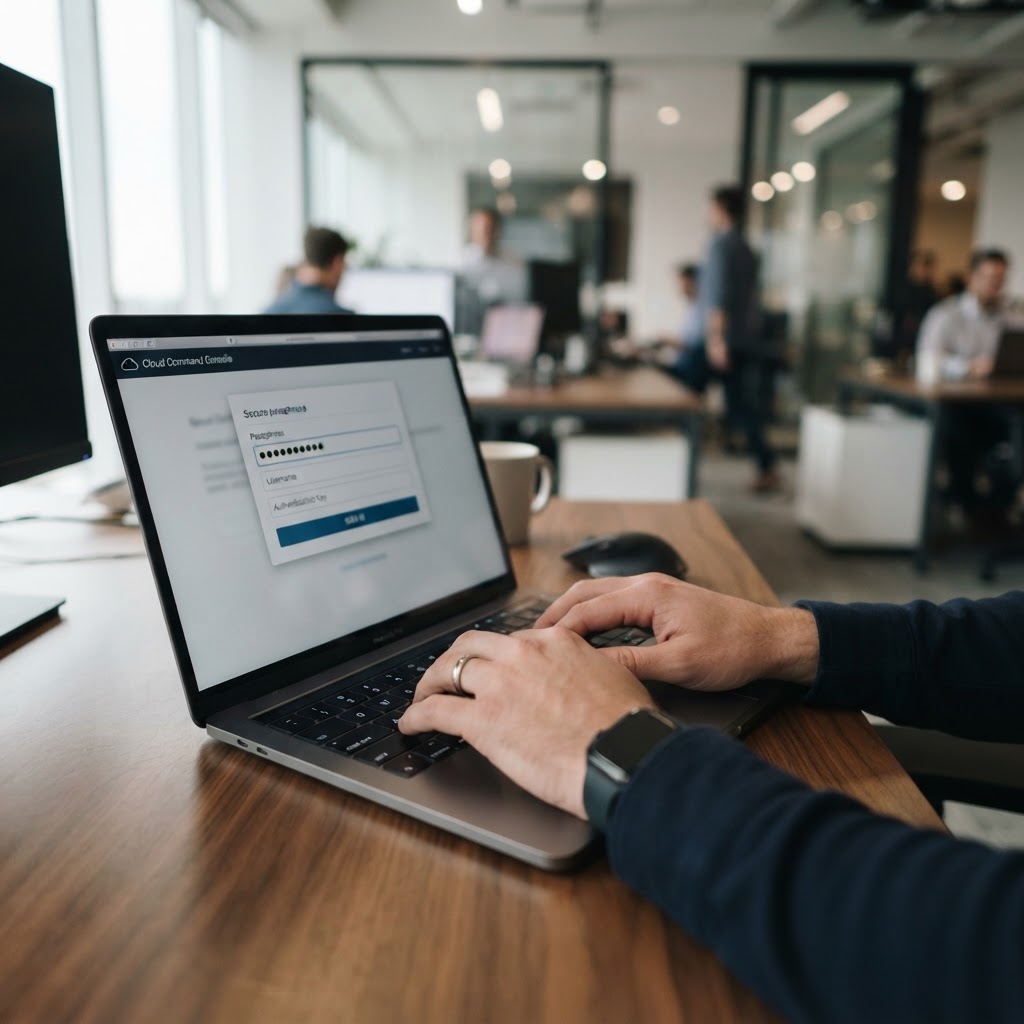
Prioritizing length with a sequence of random words makes administrative portals significantly harder for unauthorized users to access.
Within our environment, if you are setting up a client router or a surveillance NVR (Network Video Recorder), you must never use the default credentials provided by the manufacturer. If a device has a default password like "admin" or "1234," it is essentially public knowledge. You must change these to unique, high-entropy passphrases immediately. We utilize password managers, specifically Bitwarden or LastPass, to store these credentials. You should never write these passphrases on sticky notes or store them in unencrypted spreadsheets.
If you are configuring a system that requires a specific format, ensure that you always meet the maximum length allowed by the system rather than the minimum required.
Worked example
Imagine a customer calls, frustrated because they cannot secure their new office surveillance system. They tell you they set the password to "Pass1!" because it was easy to remember. This is the wrong handling. If you accept this, you leave the customer vulnerable to botnet scanners that target common passwords. The right handling is to explain why "Pass1!" is unsafe due to its low entropy and short length. You should walk them through the creation of a passphrase.
Suggest they combine four random words that mean something to them but are unrelated to their business, like "Mountain-Table-Glass-Pencil." Tell them to verify if the camera software allows for spaces or hyphens, as these further increase security. By the end of the call, the customer has a 20-character passphrase that they can remember easily, and their network hardware is protected against automated brute-force scripts that would have breached "Pass1!" in milliseconds.
Using four random, unrelated words creates a secure, long passphrase that is both strong and easy to memorize.
Where people go wrong
First, people fall for the "complexity trap," which is the belief that using eight characters with one symbol makes a password strong. In reality, modern computing power can crack an 8-character string almost instantly. Avoid this by prioritizing length above all else. Second, employees often reuse the same passphrase across multiple platforms. If one system is compromised, every account you manage becomes exposed. Never recycle passwords between your internal login, your email, and your client portal access.
Third, people rely on patterns that are too easy to guess, such as using their own name, the company name, or simple sequences like "12345." Even if these are long, they are easily guessed through "dictionary attacks," where software tries common words and name combinations. Finally, users fail to update default credentials on hardware. Never leave a manufacturer default in place, even if you think the device is not connected to the open internet.
Key takeaways
Prioritize length over complexity; always aim for at least 16 characters in any password or passphrase. Use a string of three or more unrelated, random words to ensure high entropy that stops brute-force attacks. Never reuse a passphrase across different systems or client portals. Always change default passwords on every piece of hardware or software you deploy. Use an approved password manager to keep your credentials secure and organized.