
Securing Business Networks: The Default Credential Protocol
If a device is installed with its factory-set credentials, it acts as an open door for malicious actors to infiltrate your entire corporate network.
Why this matters
If a device is installed with its factory-set credentials, it acts as an open door for malicious actors to infiltrate your entire corporate network. Hackers actively scan the internet for these known combinations, leading to data breaches, ransomware deployment, and the total compromise of your customer's professional reputation.
The core idea
Default credentials refer to the standard, factory-shipped username and password combinations assigned to hardware devices like routers, IP cameras, switches, and voice-over-IP phones. Because these credentials are hardcoded by manufacturers for ease of initial setup, they are universally documented in public manuals and online databases. Unauthorized users leverage these lists to gain administrative access to your equipment. When you leave a device in its out-of-the-box state, you are essentially leaving a key under the doormat that every potential intruder knows to look for.
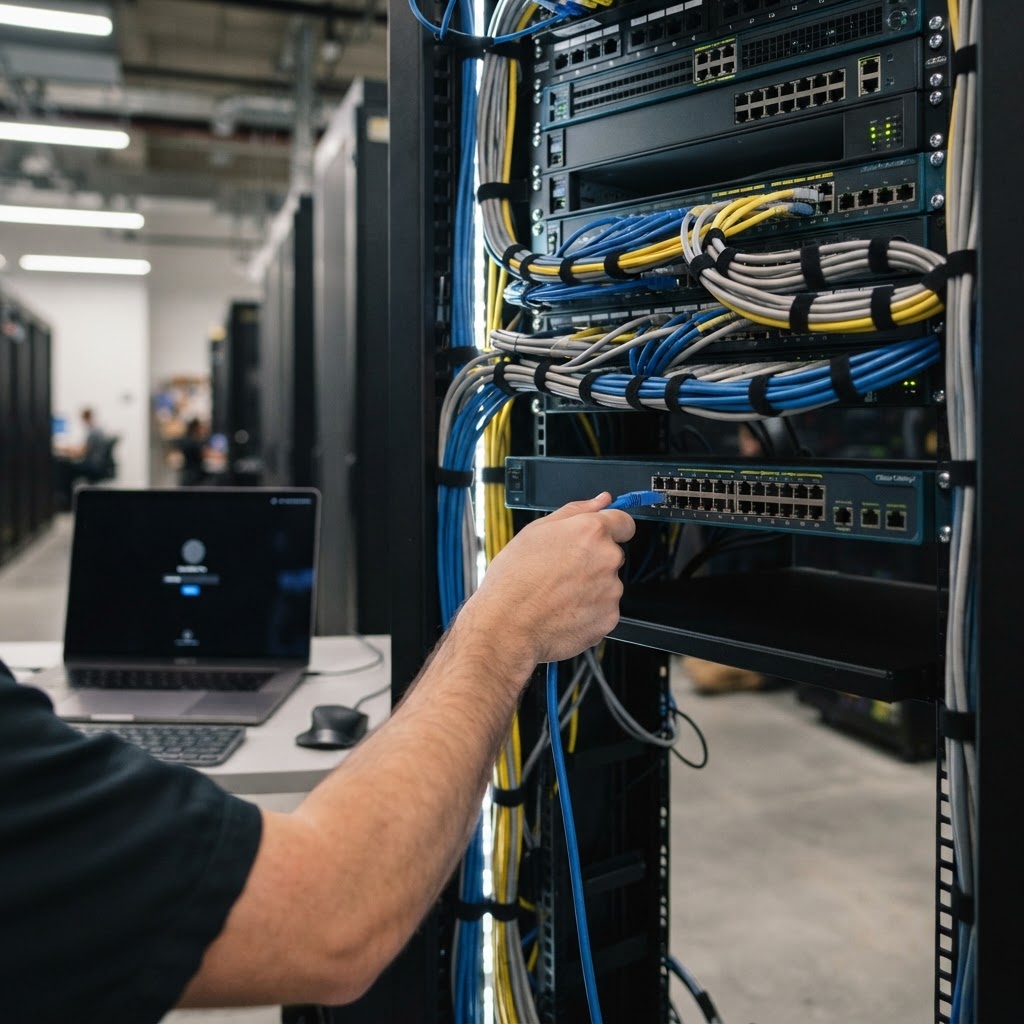
Hardware devices like network switches must be secured immediately upon installation to prevent unauthorized administrative access.
Security best practice requires you to treat the initial setup as incomplete until these credentials have been replaced with complex, unique identifiers that meet modern complexity standards.
How it works in practice
Whenever you deploy a new piece of hardware, you must perform a credential audit during the provisioning stage. This applies to every piece of equipment, from high-end enterprise firewalls manufactured by Cisco or Fortinet to basic office peripherals like network-attached printers or smart thermostats. First, consult the manufacturer's technical documentation to identify the default login details provided in the box. Second, access the device's web-based management interface through its IP address. Before you configure any other settings, navigate immediately to the 'System' or 'User Management' tab to update the administrative account.
You must set a password that is at least 16 characters long, incorporating a mix of uppercase and lowercase letters, numbers, and symbols. For enterprise-grade deployments, integrate these devices with a centralized identity management system like Active Directory or Okta wherever possible. If you are working with smaller systems, utilize a secure password manager to store the new, unique credentials for every individual device, rather than reusing a master password across the entire customer infrastructure.
Document these changes in your service ticket logs and ensure the customer receives the updated credentials in a secure format, ideally through an encrypted document portal rather than via unencrypted email.
Worked example
Imagine you are assisting a medical clinic with the installation of five new high-definition IP security cameras. You finish the physical mounting, plug in the power, and verify the network connection. The customer is eager to start monitoring, so you quickly pull up the web interface, confirm the video feed works, and tell them the system is ready to go. You leave the cameras with their default 'admin/admin' credentials because the clinic staff wants to access them quickly from their smartphones.
One week later, the clinic reports that their cameras are broadcasting patient areas to a public website, and their entire network is crawling because the devices were hijacked as part of a botnet. Now, look at the correct approach: After verifying the video feed, you immediately stop the process. You explain to the clinic manager that the cameras must be secured against external access. You open the administration menu, generate a unique, cryptographically strong password for each camera using your password manager, and apply those settings.
Taking the time to manually secure devices protects your client's infrastructure from being compromised by external threats.
You then verify that the remote access ports are configured behind a VPN rather than exposed directly to the public internet. You leave the client with a secure list of the new passwords, ensuring they are the only ones with administrative control. The result is a robust, secure deployment that protects the patient data and the clinic's digital infrastructure.
Where people go wrong
The most common error is prioritizing convenience over security, such as registering a device for a warranty or a software feature before finalizing its security settings. People often assume that the device's internal software update will prompt them to change the password, but this is rarely the case. Another frequent mistake is 'password reuse,' where you assign the same 'custom' password to every device in a fleet because it is easier to remember; if one device is compromised, the entire fleet falls.
Finally, installers often fail to remove secondary 'guest' or 'support' accounts that may exist alongside the primary admin account, leaving a back door open. To avoid these traps, treat every piece of network hardware as a potential security risk until it has been explicitly hardened by your own hand.
Key takeaways
Never consider a device installation complete until all default factory passwords have been replaced with complex alternatives. Use a reputable password manager to generate and store unique credentials for every individual device on a network. If a device does not support complex passwords or does not allow you to change the default username, report it to your supervisor as a potential security vulnerability. Keep administrative interfaces off the public-facing internet by utilizing VPNs or secure remote access gateways. Always audit your work by checking that 'guest' or 'default' user accounts have been disabled or locked.