
Understanding Firmware Security for Network Infrastructure
When you fail to treat firmware updates as a core security requirement, you leave your customers’ networks wide open to automated attacks that can compromise sensitive corporate data.
Why this matters
When you fail to treat firmware updates as a core security requirement, you leave your customers’ networks wide open to automated attacks that can compromise sensitive corporate data. Ignoring these updates transforms standard business technology, such as routers and IP cameras, into permanent backdoors for malicious actors to infiltrate entire enterprise environments.
The core idea
Firmware is the low-level software that is permanently programmed into a hardware device, acting as the bridge that allows the physical electronics to communicate with your operating system or network. Unlike traditional software applications like a web browser, firmware lives on the device itself and controls its fundamental operations, such as how a router routes traffic or how a security camera processes a video signal. A firmware update is essentially a specialized code modification deployed by the manufacturer to refine these operations.
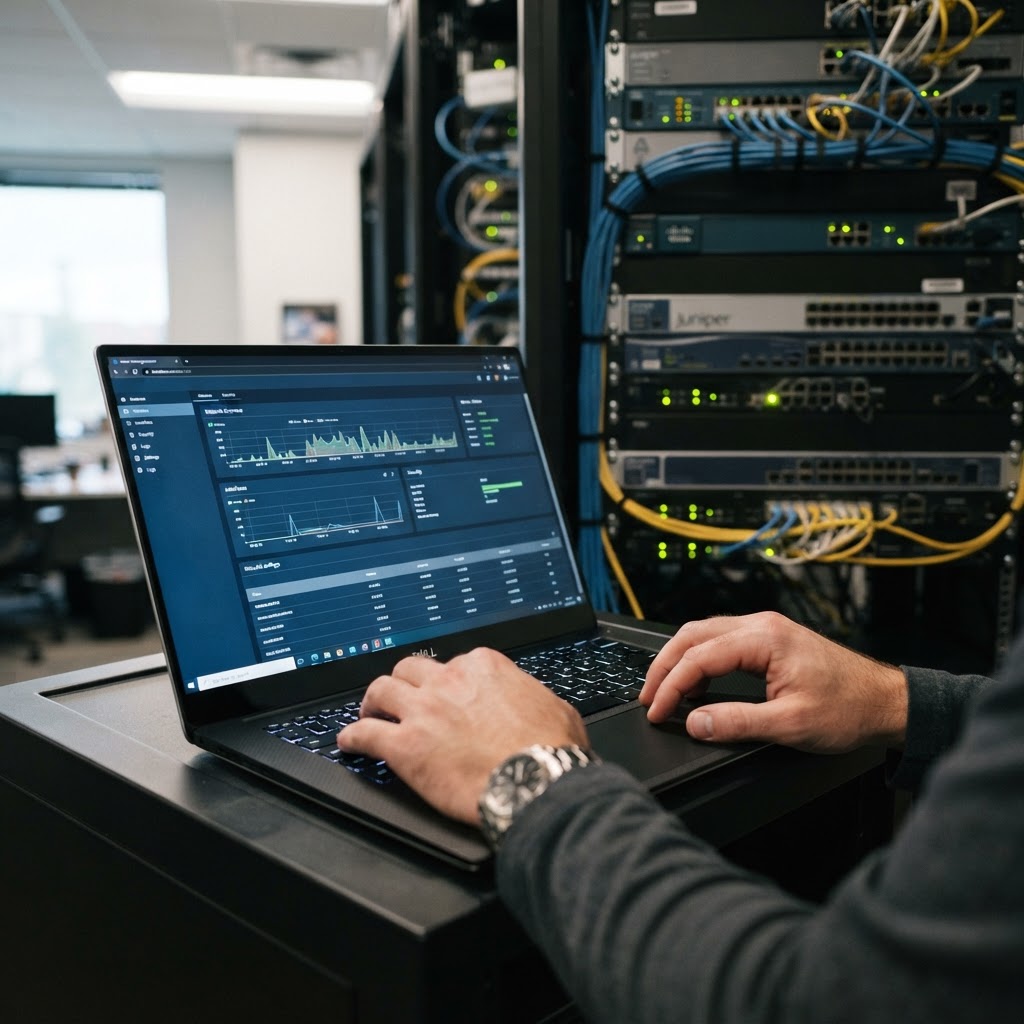
Administrative dashboards allow you to bridge the gap between physical hardware and internal control software.
When we talk about firmware in a cybersecurity context, we are primarily concerned with security patches. A patch is a piece of software designed to fix a vulnerability or security flaw found within the existing code. Because hackers constantly scan the internet for devices running outdated versions of firmware, they specifically look for systems that have not been patched to fix known exploits, which are techniques used to take unauthorized control of a device. Keeping firmware current ensures that you have successfully plugged these security holes before an intruder can crawl through them.
How it works in practice
In our distribution ecosystem, every device—from Cisco Meraki gateways to Yealink IP phones and Hikvision surveillance systems—requires a consistent lifecycle management strategy. First, you must identify the current firmware version through the device’s administrative dashboard or a centralized management platform like the Cisco Meraki Dashboard. Second, always verify the latest version against the manufacturer’s official support portal. Never download firmware from third-party forums; obtain it exclusively from the vendor’s authenticated site to prevent installing malware-laden code.
Third, establish a recurring schedule for updates, ideally during low-traffic maintenance windows, as many devices will need to reboot, causing temporary downtime. For major enterprise deployments, utilize automated deployment tools provided by the manufacturer, such as the Poly Lens management platform or similar cloud-based management software, to push updates to hundreds of units simultaneously. Always document the firmware baseline as part of your project sign-off documentation, ensuring the customer understands that these devices are living assets requiring periodic attention to remain secure against evolving threats.
Worked example
Imagine you are on a support call with a regional law firm using a fleet of legacy VoIP gateways. The customer complains that the systems are sluggish. The wrong way to handle this is to advise them that the hardware is simply aging and that they need to wait for a full hardware replacement in three years. This ignores the possibility that an outdated firmware version is causing resource leaks or, worse, failing to protect against a known exploit targeting the gateway’s SIP port. The right way to handle this is to first ask for the current firmware version installed on their hardware.
Once you confirm they are running code from two years ago, you search the manufacturer’s advisory database, which reveals a critical security patch addressing unauthorized access vectors released eighteen months ago. You then guide the client through the process of backing up their current configuration file, downloading the verified firmware from the official vendor support site, and applying the patch. By the end of the call, you have not only improved the system performance but also secured their gateway against a critical vulnerability, significantly elevating the security posture of their entire office.
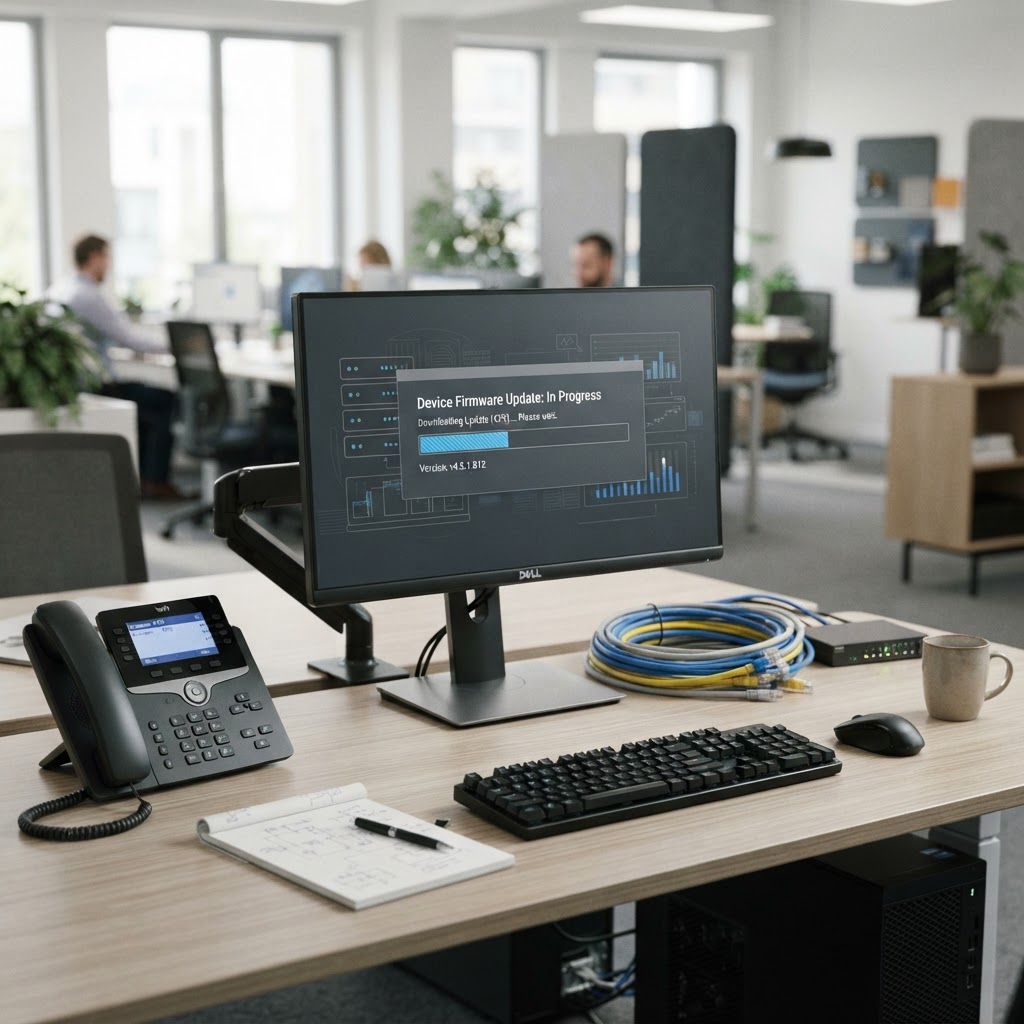
Applying security patches is a methodical process that safeguards your client's existing business technology infrastructure.
Where people go wrong
The most frequent mistake is the misconception that firmware updates upgrade the actual hardware components inside the device; remember, software can optimize performance, but it cannot change the physical capabilities or internal specs of your gear. Another common error is the set-it-and-forget-it mentality, where technicians install a device during a rollout and never return to check for updates, assuming the device remains secure indefinitely.
A third major error is skipping updates due to a fear of downtime; while reboots are necessary, the risk of a permanent network compromise due to an unpatched exploit far outweighs a ten-minute maintenance outage. Finally, never perform firmware updates without taking a backup of the device configuration first, as a failed update can occasionally reset a device to factory defaults, wiping out custom network settings and causing unnecessary recovery headaches.
Key takeaways
Firmware is the permanent software controlling your hardware functionality, not a physical component upgrade. Security patches within firmware updates act as shields against known hacker exploits. Always verify firmware versions through the manufacturer’s official support portal to ensure legitimacy. Create a documented maintenance schedule for all customer hardware to keep security patches current. Always back up existing configurations before triggering a firmware installation to prevent potential data loss. When a device exhibits performance issues, checking for a firmware update should be your primary diagnostic step.